AI agents are not tiny employees, but they can still save real work
An agent is a model wrapped with tools, memory and a loop. That makes it more useful than a chatbot and more dangerous to trust without guardrails.
The phrase AI agent is carrying far more weight than it should. Some demos make it sound as if a small digital worker has arrived, ready to plan your week, book the trip, clean the inbox and negotiate the bill. The reality is more useful and less dramatic. An agent is a language model put inside a loop: it observes the task, makes a plan, calls tools, reads the result and decides what to do next. That loop can remove tedious steps from research, scheduling, coding and operations. It can also wander, repeat itself, call the wrong tool or turn a bad assumption into several bad actions. The question is not whether agents are real. It is where the loop is narrow enough to trust.
- An agent acts, while a chatbot mostly answers
- The core loop is observe, plan, act and check again
- Tools are the hands, memory is the notebook
- A travel booking example shows where the value is
- Multi-agent systems are a division of labor
- Where agents fail first: vague goals and open tools
- The best first use is low-stakes and reviewable
- Give permissions like you would give keys
- The real test is whether the workflow is easier to supervise
- Which agents you can actually use in September 2026
- What the makers themselves say not to hand over
- If an agent has already done something wrong
- How should employees think about an AI agent enhanced workplace?
- Four assumptions that get agents into trouble
- FAQ
This is for you if
- You have seen agent demos and want to know what is actually new.
- You are considering an AI workflow for research, support, coding or personal admin.
- You want safety rules before giving a model access to tools or accounts.
Skip this if
- You want a vendor ranking or a build-your-own framework tutorial.
- You need enterprise procurement advice for a specific platform.
- You are looking for a fully autonomous assistant that can be trusted with money or private accounts.
An agent acts, while a chatbot mostly answers
A chatbot returns text. An agent can be connected to tools: a browser, calendar, email draft, code runner, database query, ticket system or file search. It uses the model to decide when to call those tools and how to respond to the results.
That does not make it independent in a human sense. It is still following patterns and instructions. The difference is that a mistake can now leave the chat box and touch your workflow. That is why agents feel powerful and why the guardrails matter.
The core loop is observe, plan, act and check again
Most agent systems repeat a small loop. They inspect the goal and available context, create a plan, choose an action, observe the tool output, then update the plan. The loop may run twice for a simple task or dozens of times for a complex one.
The loop is useful because many real tasks are not one-shot prompts. Booking travel, triaging support tickets or updating a spreadsheet requires reading intermediate results. The weak point is the same: if the plan is wrong early, the next actions can build on the wrong base.
Tools are the hands, memory is the notebook
Tool access gives an agent reach. Memory gives it continuity. A customer support agent might remember the last ticket, a research agent might save useful documents, and a coding agent might keep a list of files it already changed.
Both also increase risk. A tool can send the wrong email, delete the wrong file or trust a malicious page. Memory can store a private detail you did not intend to reuse. The question is what it is allowed to do without review.
A travel booking example shows where the value is
Imagine asking for a trip next Thursday. A basic chatbot can suggest flights if you paste details. An agent might check your calendar, search flights, compare travel windows, draft a hotel shortlist and ask before purchase. The saved time is fewer manual hops.
The last step still matters. Payment, passport details, cancellation terms and personal preferences are high-stakes enough to require a human click. A good agent workflow stops at the point where judgment, money or irreversible action enters.
Multi-agent systems are a division of labor
Some products split work among several agents: one researches, one writes, one checks, one formats. This can help because each role has a narrower instruction set. It can also produce theatre: several model voices agreeing with one another without adding evidence.
The useful version is boring. Give one worker a bounded job, give another a checklist, and compare outputs. The risky version is a pile of agents chatting until the transcript feels impressive. More agents do not automatically mean more truth.
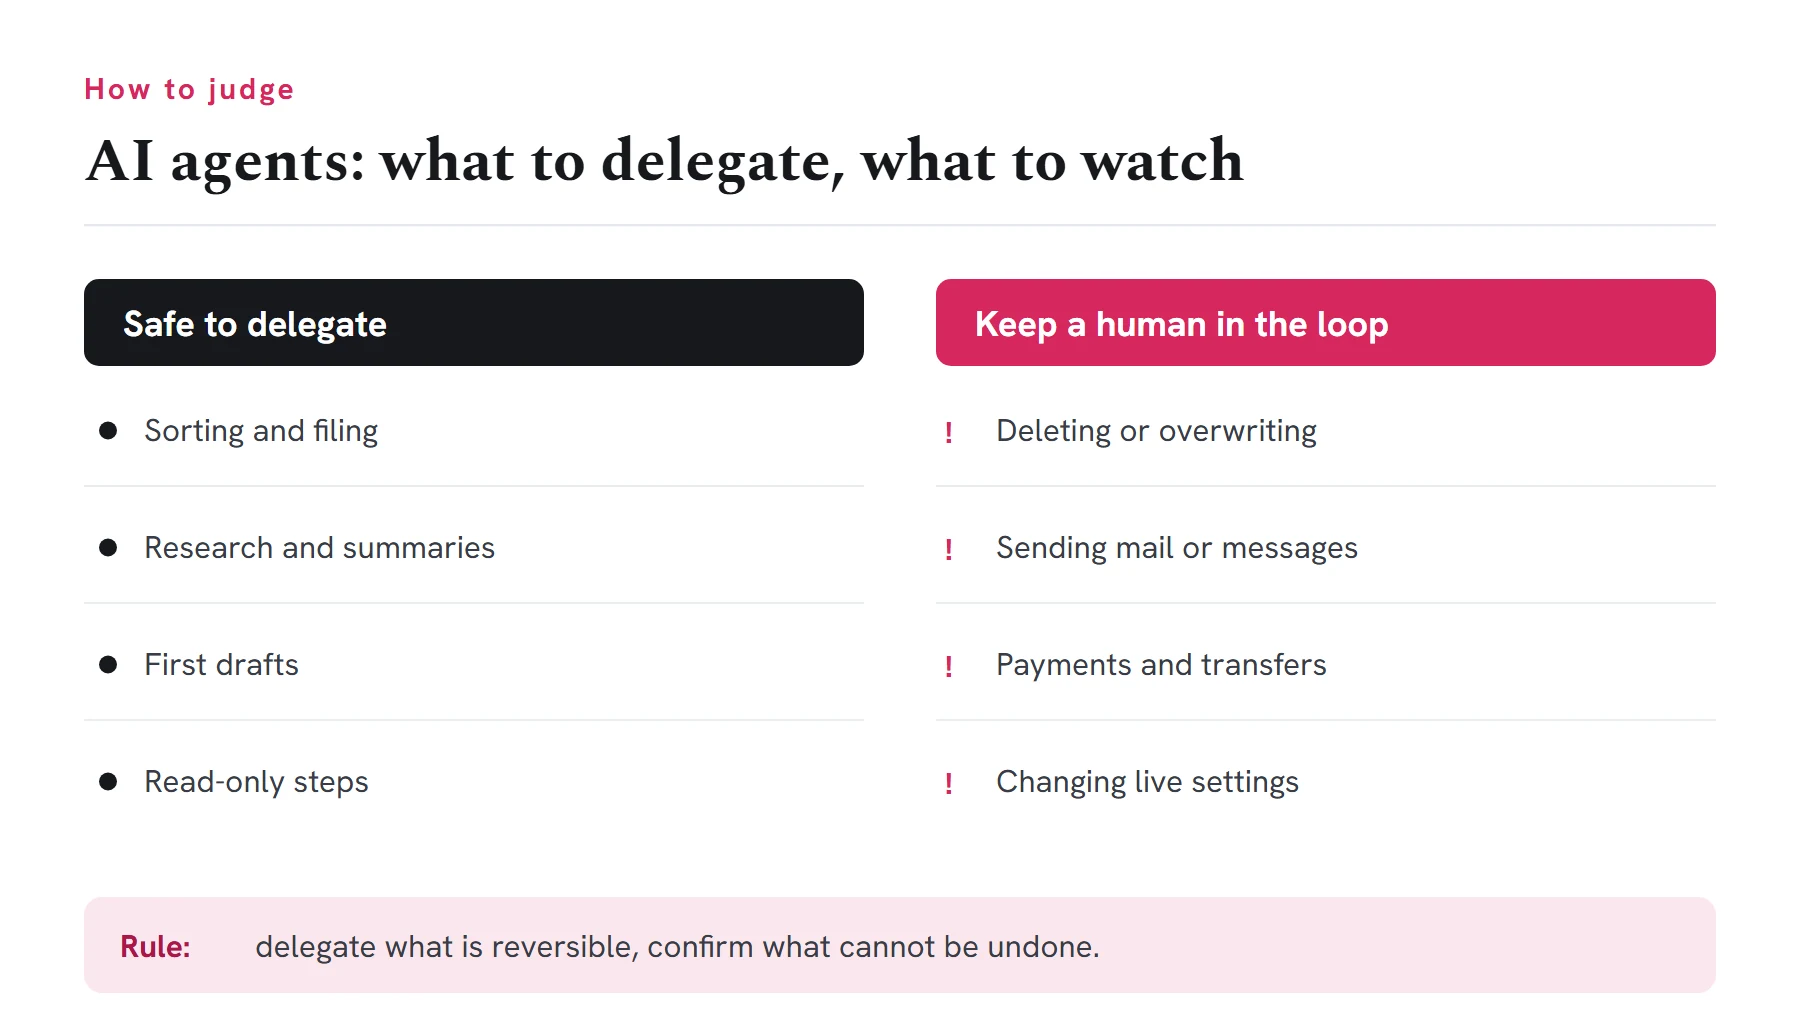
Whether you can let an agent run on its own depends less on how smart it is than on how easily its mistakes can be undone. Hand it the reversible work freely. Anything that deletes, edits or sends with no way back needs a human to confirm first.
Where agents fail first: vague goals and open tools
Agents struggle when the goal is broad, success is subjective or the tool environment is messy. Make my business better is too open. Read these ten support tickets and group them by issue is closer to useful.
They also fail when pages contain misleading instructions, when APIs return unexpected data, or when a tool action cannot be undone. Prompt injection is a real problem: a page or document can try to tell the agent to ignore your instructions.
The best first use is low-stakes and reviewable
Start with tasks where the agent produces drafts, lists, classifications or proposed actions. Research summaries, meeting prep, file organization suggestions and code refactor plans are good candidates. The output is visible before anything irreversible happens.
Avoid first experiments that involve sending messages, spending money, moving assets, deleting records or changing security settings. Those may become possible later, but only after the agent proves itself in a narrow, logged workflow.
Give permissions like you would give keys
Permissions should be small, temporary and specific. Read-only access is safer than write access. A test calendar is safer than your main calendar. A sandbox database is safer than production. A draft email is safer than auto-send.
Logs are part of trust. You should be able to see what the agent saw, what tool it used, what it changed and why. If a system cannot show an audit trail, it is not ready for important work.
The real test is whether the workflow is easier to supervise
The best agents do not remove the human. They make the human review easier. They gather the scattered pieces, propose the next step and surface the places that need judgment. That is already valuable.
If using the agent creates a new job of watching a wandering process, the tool has not helped. Keep the loop short, the permission small and the review visible. That is where agents stop being hype and become machinery.
| Use case | Good first version | Stop point |
|---|---|---|
| Research brief | Collect sources and summarize claims | You verify the key source. |
| Inbox triage | Label and draft replies | You approve sending. |
| Calendar planning | Suggest windows and conflicts | You confirm bookings. |
| Code maintenance | Propose edits and run tests | You review the diff. |
| Financial or legal action | Prepare questions only | A qualified person decides. |
- Define a narrow task with a visible success condition.
- Start with read-only or draft-only permissions.
- Require a human confirmation before money, messages, deletion or account changes.
- Keep logs of tool calls and outputs.
Which agents you can actually use in September 2026
Names change fast, so this list sticks to products with an official page or solid reporting behind them as of September 2026. It is not a ranking. The column that matters most is the last one: where the agent stops and asks you.
| Product | What it does | Where it stops |
|---|---|---|
| ChatGPT Work and ChatGPT agent (OpenAI) | ChatGPT Work, launched in July 2026, builds presentations, spreadsheets and other documents from your connected apps and files. The earlier ChatGPT agent, released in July 2025, works in a virtual computer to browse and fill in forms. | ChatGPT agent asks permission before consequential actions such as purchases or sending email, and takeover mode lets you type passwords yourself. Before using Work, check which apps it is connected to. |
| ChatGPT Atlas (OpenAI) | A browser released in October 2025 with an agent mode that takes actions on websites. | You can interrupt or redirect it while it works. |
| Claude in Chrome (Anthropic) | A Chrome extension on paid Claude plans (Pro, Max, Team, Enterprise) that reads pages, clicks and fills in forms. | Defaults to Automatically approve, pausing when it judges your approval is needed; switch to Manually approve to review every action. |
| Auto browse in Chrome (Google Gemini) | In preview for Google AI Pro and AI Ultra subscribers in the US; handles multi-step tasks across websites. | Pauses for your confirmation, or hands the step to you, before things like a purchase or a social media post. |
If a product cannot tell you where it stops, how you halt it mid-task and where its activity log lives, keep it away from your real accounts until it can.
What the makers themselves say not to hand over
Vendor safety pages are blunter than most reviews. Anthropic's guidance for Claude in Chrome calls prompt injection, malicious instructions hidden in web content that trick the agent into unintended actions, the biggest risk for browser-using AI. It lists work the extension should not do: managing financial accounts or investments, handling legal documents or contracts, processing medical or health information, entering sensitive data, and stock trading or investment transactions.
In practice that means: no bank, payment, brokerage or crypto wallet logins for the agent. Type passwords and one-time codes yourself, never into the chat; in ChatGPT agent, switch to takeover mode first. Let it draft email but keep the send button for yourself. In Claude in Chrome, switch approval to manual. Log out of sensitive sites when the task is done. And if the agent suddenly changes topic, opens sites you never mentioned or asks for a password or code, stop the task at once, since that pattern is what a prompt injection looks like.
If an agent has already done something wrong
Stop it first. All of the products above let you interrupt or take over, and an agent left running will keep building on its mistake.
Then take the keys back. Access an agent got through a sign-in or authorization has to be removed from the account side. For a Google account, open myaccount.google.com/linkedapps, choose Access to your Google Account, pick the app, select See details, then Remove access and confirm. On GitHub, go to your profile picture, Settings, Applications, the Authorized OAuth Apps tab, and click Revoke. If the agent ever saw a password, change it.
Then undo what you can. Send a correction after a wrong email. Cancel a wrong order with the merchant, and if money has already gone, call your bank or payment provider to ask about stopping or reversing it. Look for deleted files in the trash or your cloud drive's version history. Keep screenshots of the agent's activity and the conversation; you will need them for the vendor, a dispute or a police report.
Watch for people selling "an AI agent that trades for you" in exchange for your account login or exchange API keys. Handing money and credentials to a program you cannot see into or stop is no safer than handing them to a stranger.
How should employees think about an AI agent enhanced workplace?
Think of the agent as a fast junior colleague whose work goes out under your name. What it drafts, files or sends is still yours to answer for, so the useful question is not whether it can do your job but which steps you will now review instead of doing by hand.
A few habits make that workable. Use the agents and accounts your employer has approved rather than connecting a personal tool to work email or files; approved tools usually come with admin controls, such as limits on which sites the agent may open, and yours does not. Keep client data and unpublished numbers out of anything the policy doesn't cover. Find out what the agent logs, because after a mistake the record of what it saw and did is how you tell whether the fault was the agent, the instructions or the data. Keep approval steps for money, outside messages and deletions even when the tool offers to skip them. And note which tasks you hand over and how often you had to fix the result; that list is what tells you and your manager which work is safe to automate further.
Four assumptions that get agents into trouble
It is a model-driven workflow with tools and a loop.
More autonomy without review is mostly more surface area for mistakes.
External pages can contain misleading instructions and hostile content.
Completion and correctness are different. Review remains part of the system.
FAQ
Do I need an agent for simple prompts?
No. If a single answer solves the task, a normal chatbot is simpler and safer.
What is tool calling?
It is the model choosing to use a defined function, such as search, calendar lookup or code execution.
Can agents remember my preferences?
Some can, but memory should be explicit and editable. Do not assume every detail should be saved.
What should a beginner automate first?
A low-stakes workflow that produces a draft or checklist, not a transaction.
How do I revoke an AI agent's access to my accounts?
Stop the task first. Then remove the connection from the account side. For Google, open myaccount.google.com/linkedapps, choose Access to your Google Account, pick the app, select See details and then Remove access. On GitHub, go to Settings, Applications, Authorized OAuth Apps and click Revoke. If the agent ever saw a password, change it.
Sources & further reading
- arxiv.org: Research literature on tool use and agent evaluation.
- huggingface.co: Open model and agent framework documentation.
- anthropic.com: Safety research and practical notes on tool-using models.
Updated: May 12, 2026. On September 29, 2026 we added the agents you can use as of September 2026 and where each one stops to ask you, what their makers say not to hand over, how to stop an agent and revoke its access after a mistake, and how employees can work alongside agents.

Fang Yu is the editor of FutureLens, turning published papers, official materials and public explanations into plain-language notes. He is most interested in the gap between a technology's public pitch and the evidence a careful reader can actually check. More about the author